

Decrypt From AES256
Decrypts a text that was encrypted with AES using a 256-bit key, from Base64 or Hex.
The Decrypt From AES256 action turns a text encrypted with AES-256 (for example by Encrypt To AES256 or by a partner system) back into readable text, using the same secret key and IV.
Add the action
In the Process Designer toolbox, open Converters › Cryptographic and pick Decrypt From AES256 (or type AES256 in the search box).
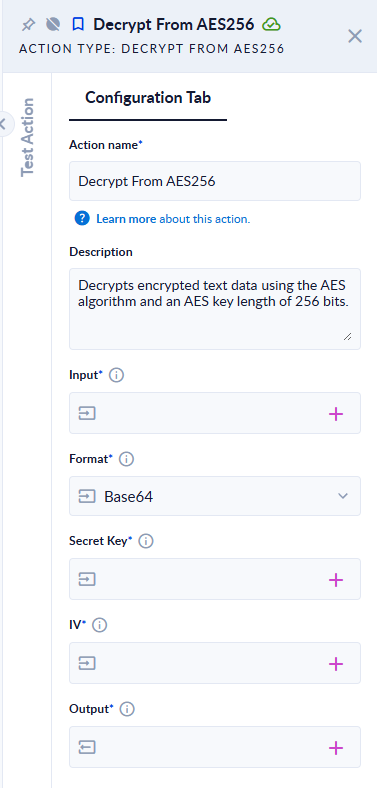
Inputs and outputs
| Field | Direction | Type | Required | What to put / what you get |
|---|---|---|---|---|
| Input | Input | Text | Yes | The encrypted text. |
| Format | Input | Option | Yes | How Input is encoded: Base64 (default) or Hex. |
| Secret Key | Input | Text | Yes | The key used to encrypt: exactly 32 characters. |
| IV | Input | Text | Yes | The IV used to encrypt: exactly 16 characters. |
| Output | Output | Text | Yes | The decrypted text. |
Example
With Secret Key 12345678901234567890123456789012 and IV 1234567890123456:
| Input | Format | Output |
|---|---|---|
7ZFkdOXkAl7PTq2sHA8knQ== | Base64 | Hello PROCESIO |
ED916474E5E4025ECF4EADAC1C0F249D | Hex | Hello PROCESIO |
7ZFkdOXkAl7PTq2sHA8knQ== with a different 32-character key | Base64 | The step fails: Padding is invalid and cannot be removed. |
Good to know
- A wrong key or IV usually fails with
Padding is invalid and cannot be removed.rather than with a message about the key. - A key or IV of the wrong length fails the step with
Input Error: Secret Key must be 32 characters long!orInput Error: IV must be 16 characters long! - The action expects AES-256 in CBC mode with PKCS7 padding, which is what Encrypt To AES256 produces. Data encrypted with another mode cannot be decrypted here.